
Qualys TotalAppSec (Web Application and API Security)
Unified DAST, API security and web malware detection that tests web apps and APIs against the OWASP Top 10 and OWASP API Top 10.
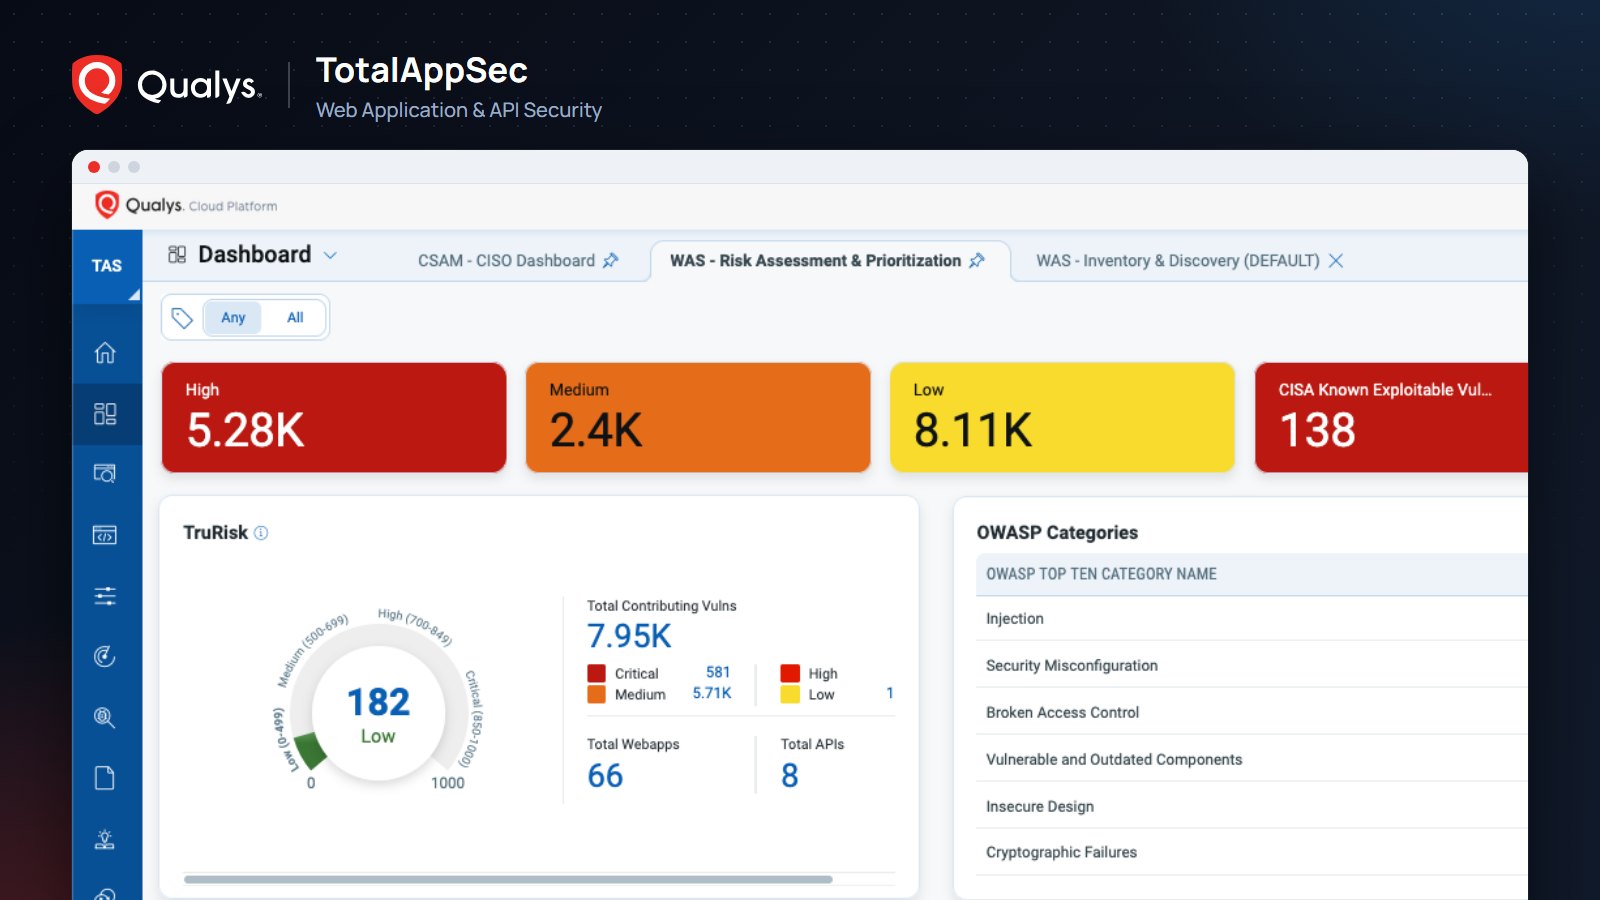
Qualys TotalAppSec (Web Application and API Security)
Secure web applications, APIs and web malware from one solution, and find the flaws before attackers do.
Web applications and APIs are the most dynamic part of your internet-facing surface; every new release and every new endpoint adds risk. Qualys TotalAppSec (TAS) unifies Web Application Scanning (WAS), API Security and Web Malware Detection in a single application security solution. It runs on the Qualys Enterprise TruRisk Platform, with findings prioritized by TruRisk.
End-to-end testing, from application to API
The TotalAppSec DAST engine discovers web applications and tests them for vulnerabilities across the OWASP Top 10 and regulatory requirements. The same solution centrally discovers and tests your APIs and detects malicious code on your websites.
- Unified DAST: Web application discovery and vulnerability testing in one solution, covering the OWASP Top 10 and regulatory requirements.
- API discovery and security testing: Centrally discovers APIs and tests them against the OWASP API Top 10 risks.
- API compliance testing: Tests APIs against the OpenAPI Specification (OAS) v3, exposing API misconfigurations and deviations from spec.
- Deep-learning web malware detection: Identifies both widespread and zero-day malware on web applications using deep-learning models.
- TruRisk prioritization: Track findings on dashboards by TruRisk score, severity and OWASP category.
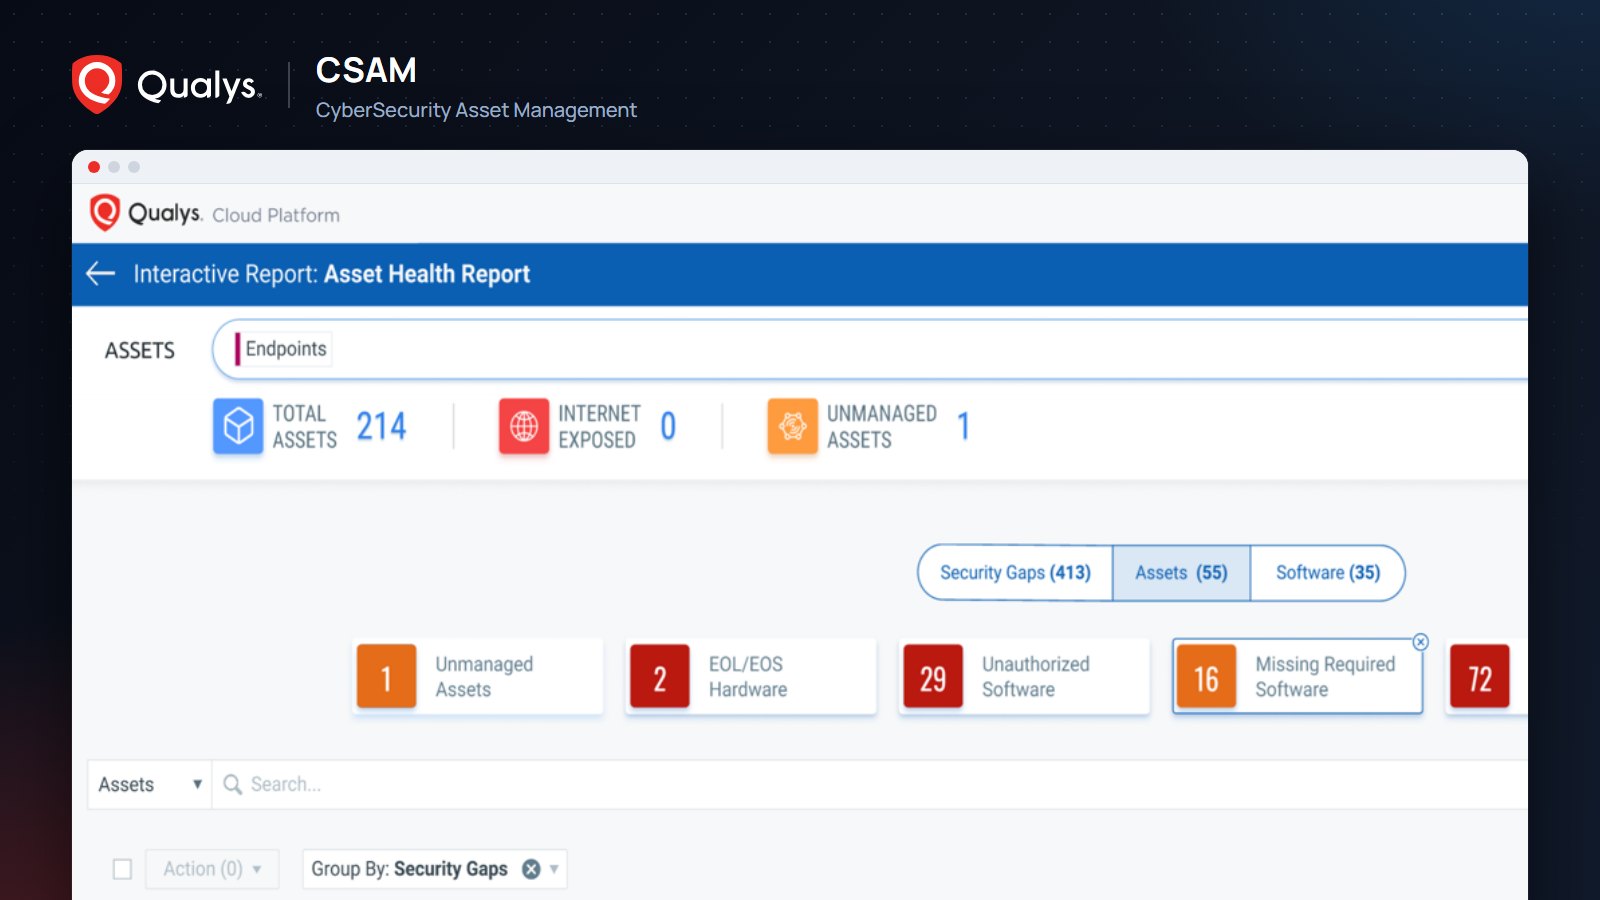
- Orchestration with CSAM: Launch web application scans directly from CSAM asset workflows.
Standards and components
- Standards: OWASP Top 10, OWASP API Top 10, OpenAPI Specification (OAS) v3.
- Components: Web Application Scanning (WAS), API Security, Web Malware Detection.
- One dashboard: Web applications and APIs are tracked in the same TruRisk view, CISA known exploited vulnerabilities are called out separately, and findings are followed through active, fixed, new and reopened states.
- Platform integration: Application security findings flow into Enterprise TruRisk Management, where they are weighed alongside infrastructure and cloud risk in the same view.
“One last check before go-live”: A new customer portal is scanned with TotalAppSec before release. Injection and access-control flaws are listed by OWASP category, the portal's APIs are validated against their OAS v3 definition, and every deviation goes straight to the development team.
Want to test your apps and APIs before attackers do?
Komtera, Qualys's distributor in Turkey, brings a technical team to help you configure TotalAppSec for your application estate. Request a demo or a POC and test your web applications and APIs in your own environment.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.