
Qualys TruRisk Eliminate (Patch, Mitigate and Isolate)
Don't just measure risk, eliminate it: patch what you can, protect what you can't patch, and quarantine at-risk assets before they're exploited.
Qualys TruRisk Eliminate (Patch, Mitigate and Isolate)
Eliminate it, don’t just measure it: patch, mitigate or isolate, all from one agent and one platform.
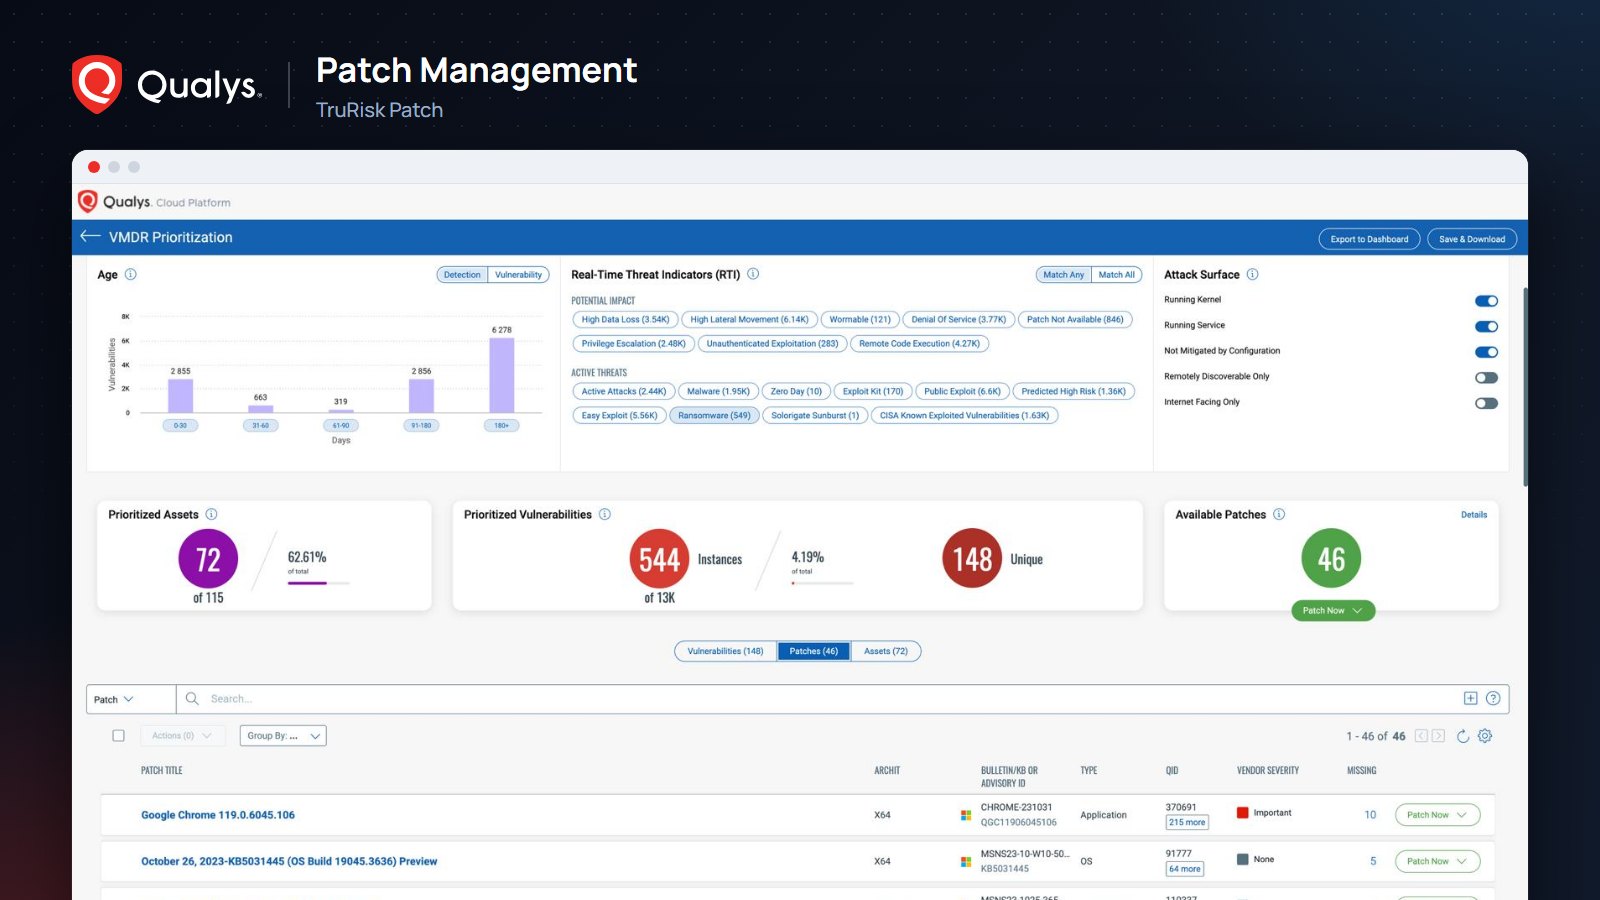
Most vulnerability programs stop at the report, leaving IT to work out the fix. Qualys TruRisk Eliminate closes that gap with three ways to remove risk: TruRisk Patch to test and deploy patches, TruRisk Mitigate for vulnerabilities that have no patch or can’t be patched safely, and TruRisk Isolate to quarantine at-risk devices. It is the “Eliminate” step of the Qualys Enterprise TruRisk Platform, built natively into the VMDR lifecycle.
One remediation workflow, from routine patching to zero-day response
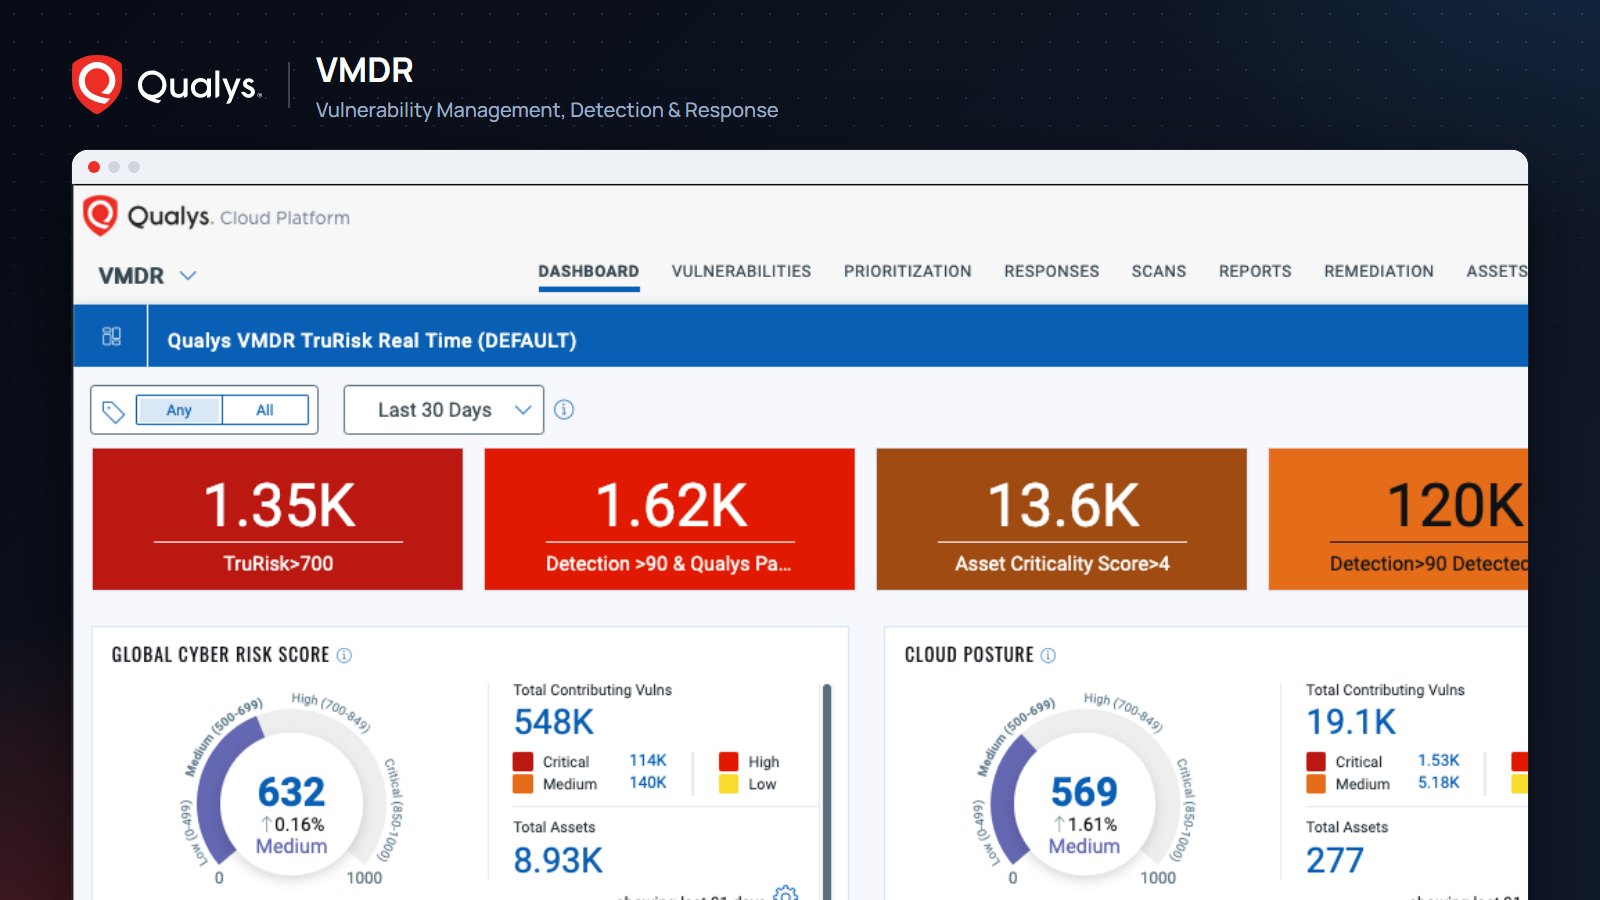
Because all three capabilities run on the same Qualys Cloud Agent and report back into VMDR, IT and security teams work from a single view, agree on priorities and shorten mean time to remediate (MTTR). Qualys reports remediation of critical vulnerabilities that is more than 40% faster on average.
- Zero-touch patching: Integrated Patch Management tests and deploys patches automatically, driven by risk rather than by the calendar.
- Remediation for the unpatchable: TruRisk Mitigate addresses vulnerabilities that have no fix yet, including zero-days.
- Proactive containment: TruRisk Isolate quarantines at-risk assets before they can be exploited.
- One agent: Every capability is delivered through the Qualys Cloud Agent you already run, with no extra software.
- Closed-loop reporting: Every patch, mitigation and isolation is reflected in VMDR reports, so remediated and mitigated risk sit side by side.
TruRisk Mitigate: what if you can’t patch it?
Some vulnerabilities have no patch yet; others live on systems where an emergency patch could cause an outage. TruRisk Mitigate applies advanced controls and scripts based on vendor, CISA and Qualys Threat Research Unit (TRU) recommendations. It maps Qualys vulnerability IDs (QIDs) to remediation actions, offers alternative mitigations where patching carries operational risk, and puts defenses in place against zero-day vulnerabilities before the vendor patch is released.
TruRisk Isolate: contain risk without losing control
TruRisk Isolate offers a proactive alternative to reactive EDR methods. It isolates a risky device from the network so its vulnerabilities can’t be exploited, while exceptions keep it reachable for remote patching and control by Qualys and other authorized resources. Isolation is delivered through Qualys Cloud Agent technology with no EDR required, and every action is captured in VMDR reports.
“Zero-day on a critical server”: A critical vulnerability is disclosed with no vendor patch. The team applies a TruRisk Mitigate control across the affected servers, isolates one already-exposed host with TruRisk Isolate while keeping it manageable, then rolls out the fix through TruRisk Patch as soon as it ships, with every step tracked in VMDR.
Ready to move from measuring risk to eliminating it?
As Qualys’s distributor in Turkey, Komtera and its technical team help you plan and roll out TruRisk Eliminate. Get in touch to schedule a demo or a proof of concept (POC) in your own environment.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.