
Qualys Multi-Vector EDR (Endpoint Detection and Response)
Endpoint detection, response and protection with ML-based antivirus against zero-day, ransomware and phishing attacks, on the agent you already run.
Qualys Multi-Vector EDR (Endpoint Detection and Response)
Protect your endpoints against attacks with the agent you already deploy.
Endpoints are where attackers most often strike, and stacking separate security tools on them adds management overhead. Qualys Multi-Vector EDR combines endpoint detection and response (EDR) with endpoint protection (EPP). It forms the threat detection and response layer of the Qualys Enterprise TruRisk Platform.
Detection and protection in a single agent
- Endpoint detection and response (EDR): Detect and respond to attacks on your endpoints.
- Endpoint protection (EPP): Protect endpoints against attacks, not just detect them.
- ML-based antivirus: Machine-learning-based antivirus helps defend against zero-day attacks, ransomware and phishing.
- One agent: Runs on the lightweight Qualys Cloud Agent used across the platform; its kernel-level component is one of only two Cloud Agent components that touch kernel space (the other is FIM).
Why one platform matters
EDR can be activated without additional installations, and its threat data feeds Qualys’s unified view of risk. That means detections are weighed alongside the vulnerability and asset context already on the same platform.
- Nothing new to install: New capabilities are switched on through the Qualys Cloud Agent, with more than 110 million agents deployed worldwide.
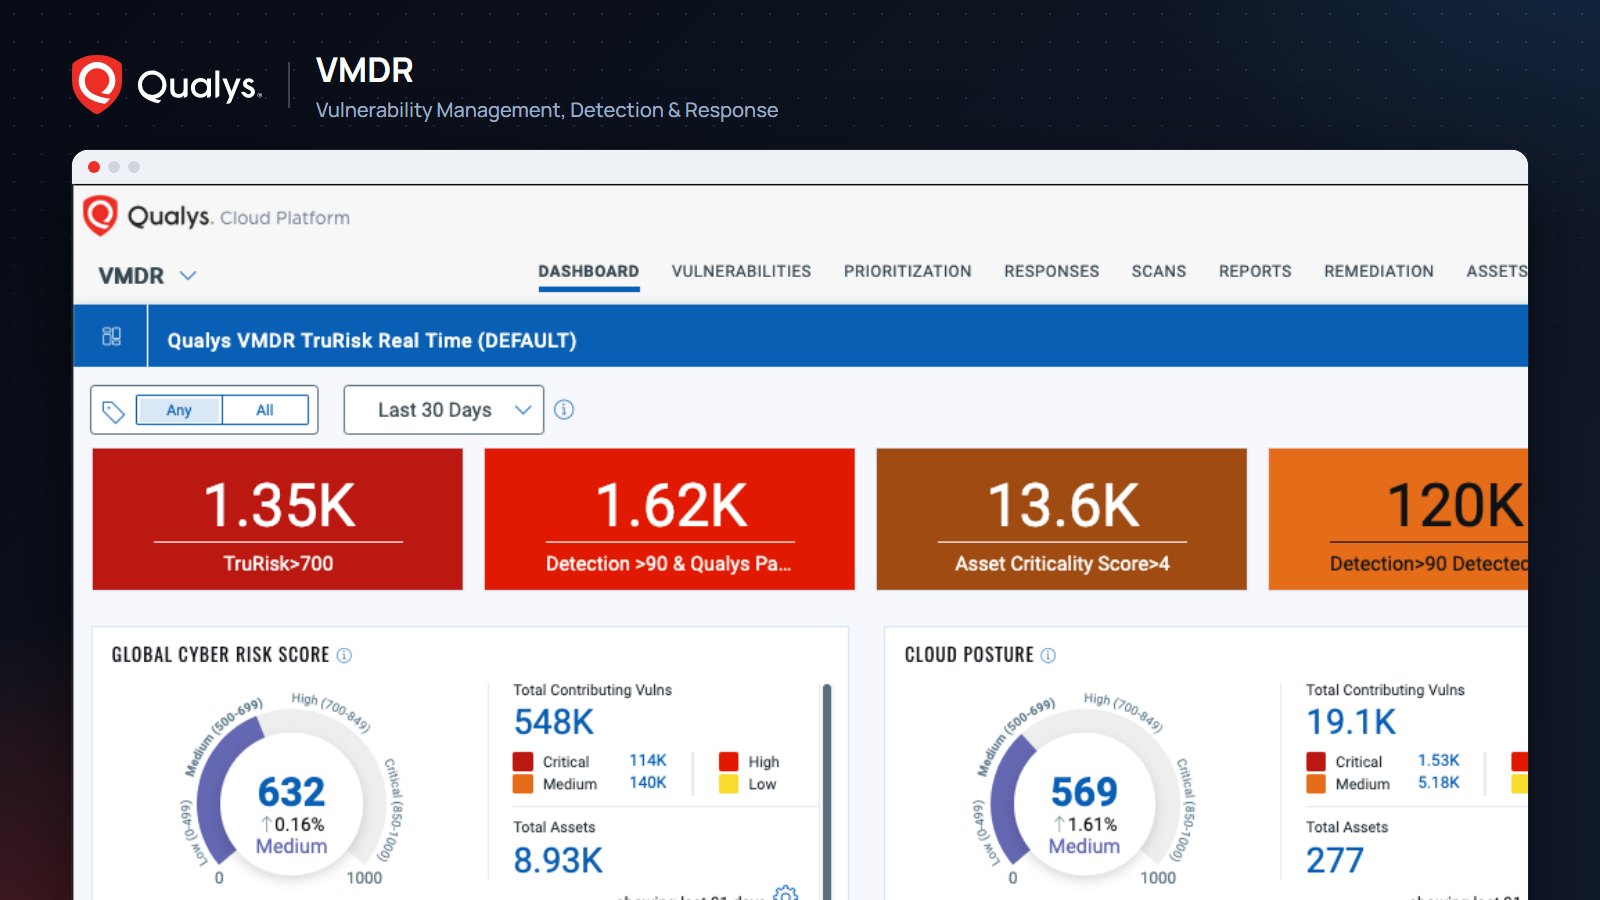
- Detection in context: Threat detection is correlated with vulnerability and asset data on one platform.
- One picture of risk: Endpoint threats become part of your organization’s unified, TruRisk-based risk view.
“Suspicious email attachment”: A user opens a malicious attachment. ML-based antivirus flags the payload, EDR surfaces the endpoint activity, and the analyst reviews the incident together with the device’s vulnerability and asset context on the same platform.
Looking to simplify endpoint security?
As Qualys’s distributor in Turkey, Komtera and its technical team help you evaluate Multi-Vector EDR. Get in touch for a demo or a POC.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.