
Qualys CSAM (CyberSecurity Asset Management)
A security-driven asset inventory that discovers known and unknown assets, enriches them with business context and exposes security gaps and tech debt.
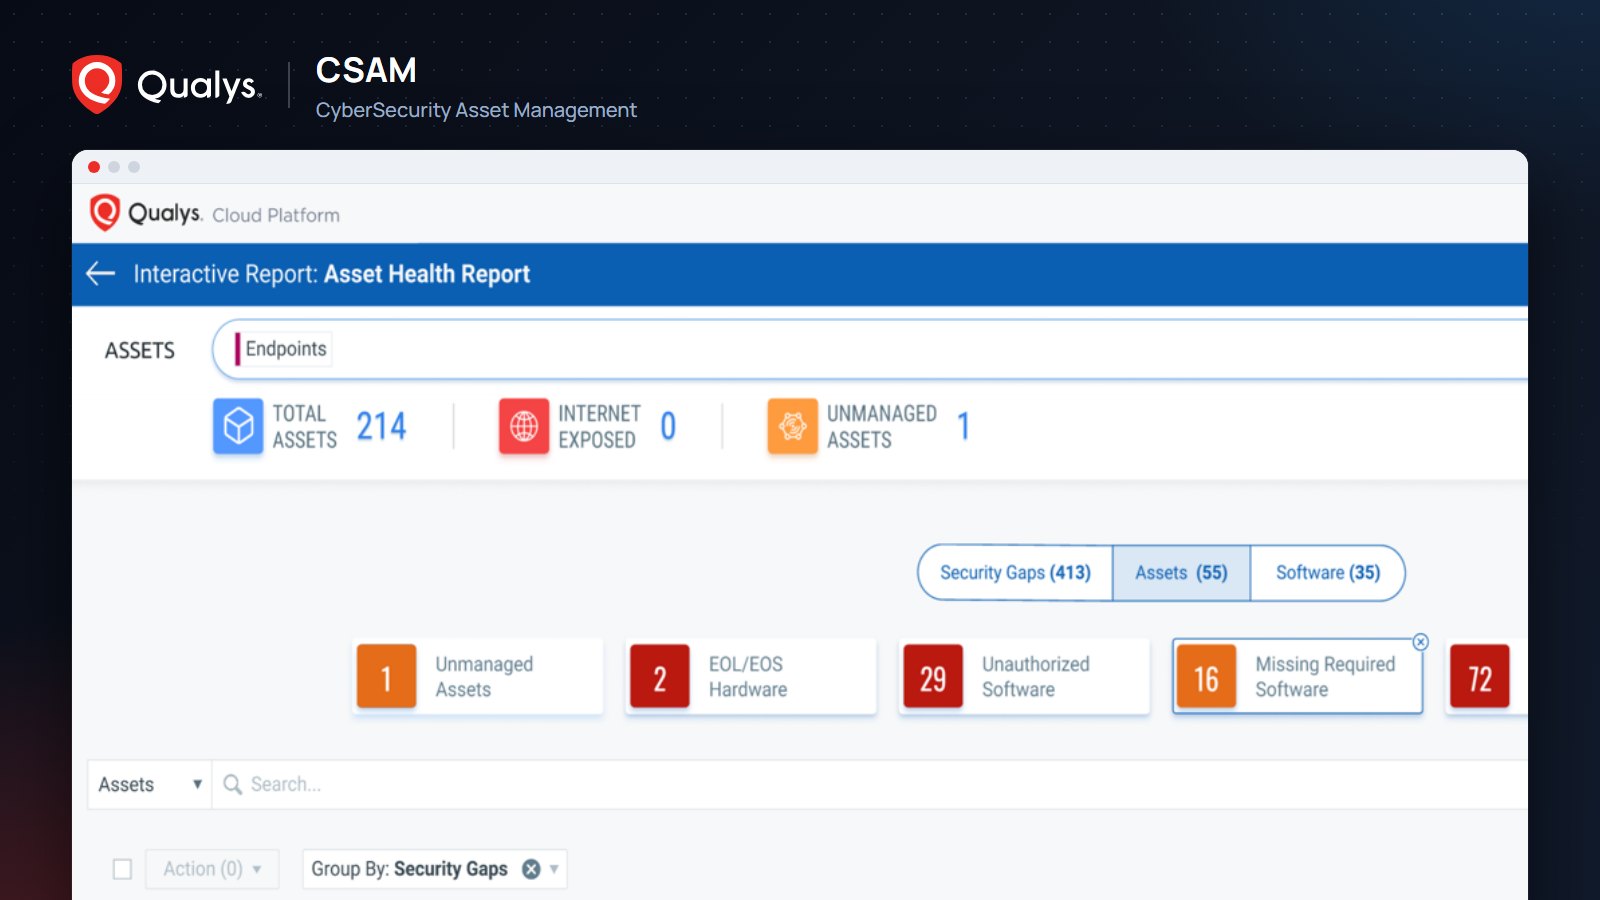
Qualys CSAM (CyberSecurity Asset Management)
You can't secure what you can't see. Qualys CSAM shows you your entire attack surface using the same intelligence attackers use.
The attack surface is expanding fast, and every unmanaged server, forgotten cloud resource and unsupported application is a new target. Qualys CyberSecurity Asset Management (CSAM) continuously discovers and classifies every asset across your on-premises, cloud and hybrid estate, so you can remediate gaps and measurably improve your security posture. It runs on the Qualys Enterprise TruRisk Platform, sharing the same Cloud Agent and sensor fabric as the rest of the platform.
Beyond the CMDB: an inventory built for security
A traditional CMDB keeps records for IT operations. CSAM is built for security teams, combining real-time discovery, TruRisk-based prioritization, deep threat context and bi-directional ITSM and CMDB integration in one inventory.
- Continuous discovery: Brings internal known and unknown assets, unknown internet-facing assets and multi-cloud resources into a single inventory.
- Security gap detection: Flags end-of-life (EoL) and end-of-support (EoS) software, unauthorized software, missing agents and security tools, unsanctioned ports and expired SSL certificates.
- Bi-directional CMDB sync: Works automatically with CMDBs such as ServiceNow, feeding them high-fidelity security data and eliminating manual updates.
- Business context: Imports business information and asset criticality from third-party sources to align security work with business goals.
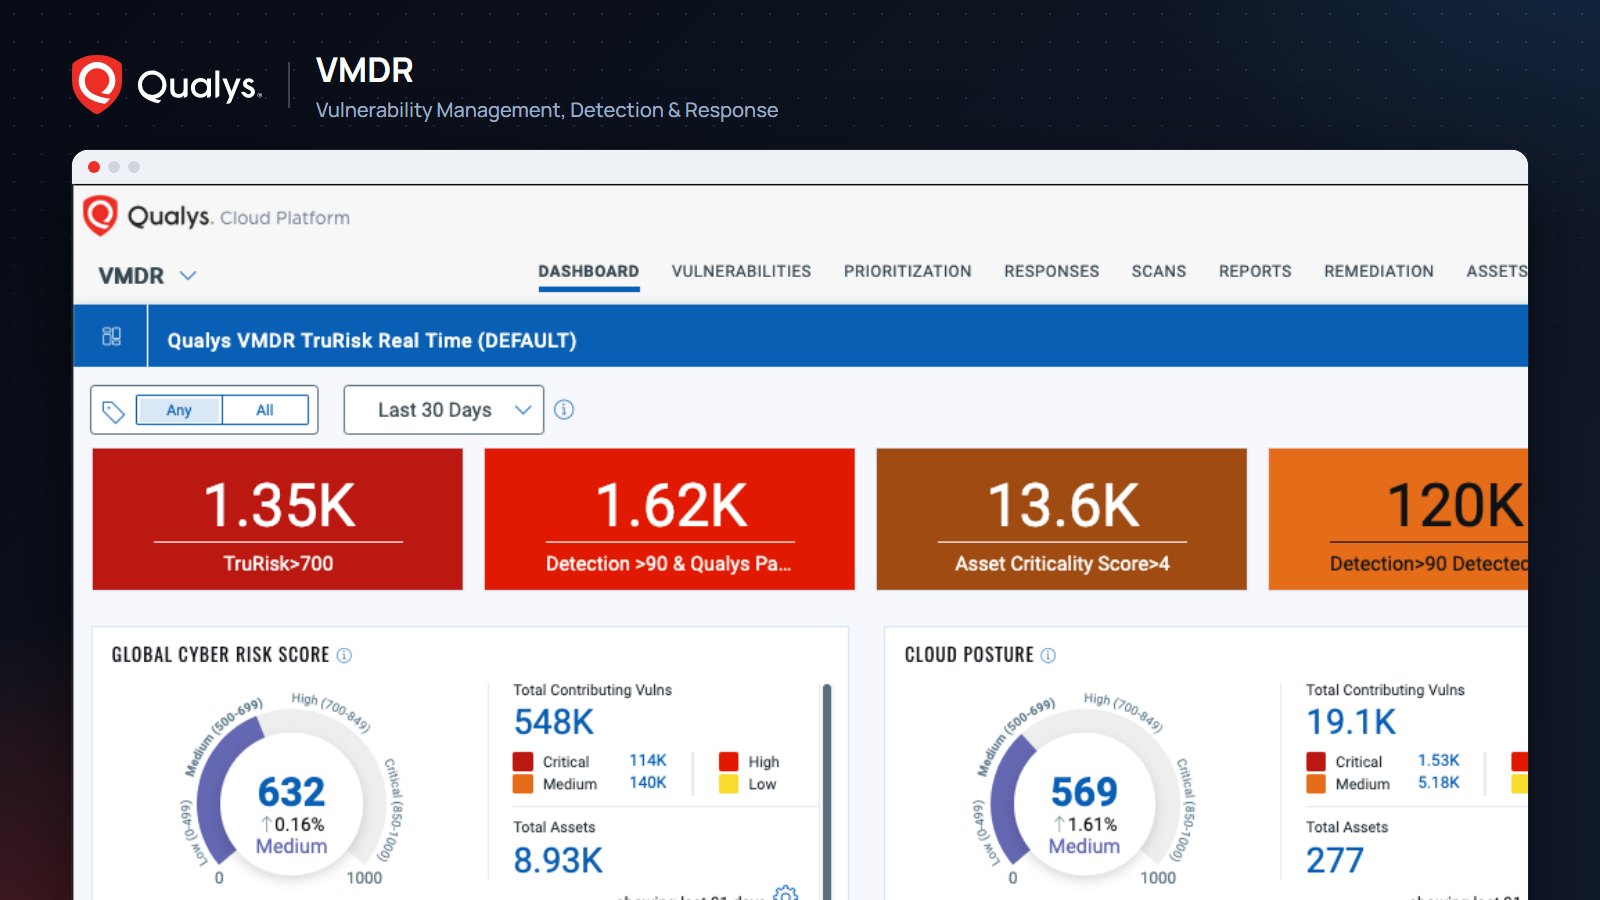
- Orchestration and automation: Launches VMDR and WAS scans, patch remediation workflows and even software uninstalls straight from the asset view.
- Tech Debt report: Highlights EoL/EoS hardware and software so you can prioritize and plan upgrades for high-risk systems that no longer receive security patches.
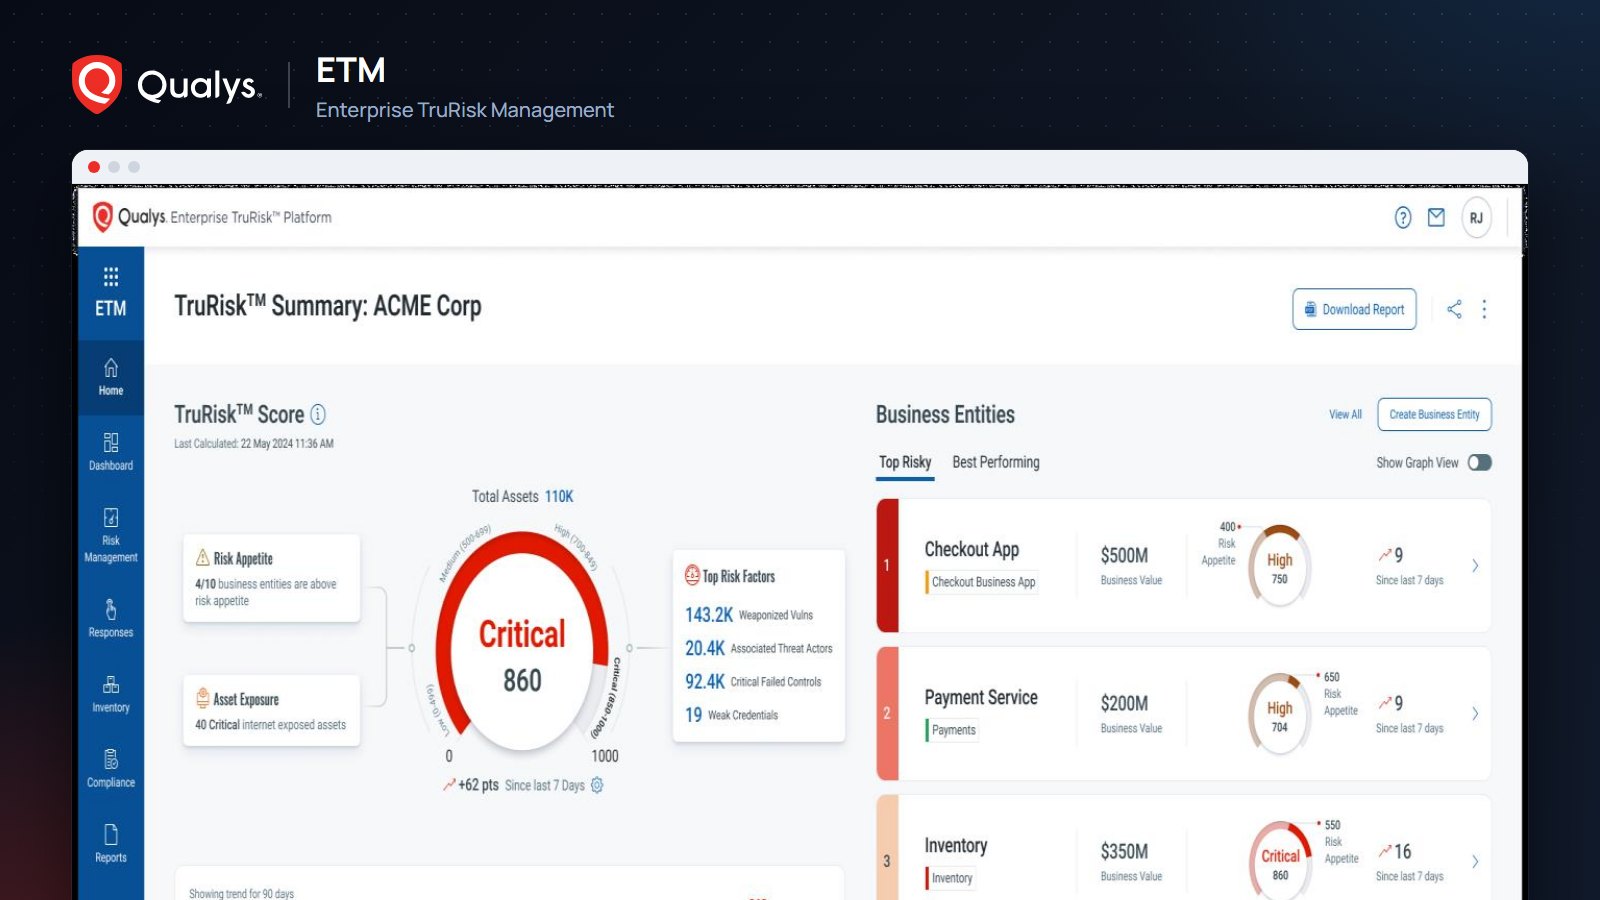
- TruRisk prioritization: Extends risk-based detection into your asset management program and quantifies cyber risk over time.
Coverage and data sources
- Environments: On-premises, cloud, container, OT/ICS and hybrid environments; software and applications; domains and subdomains.
- Data collection: Qualys Cloud Agent, network scanners, passive sensors, cloud connectors, CMDB and third-party integrations.
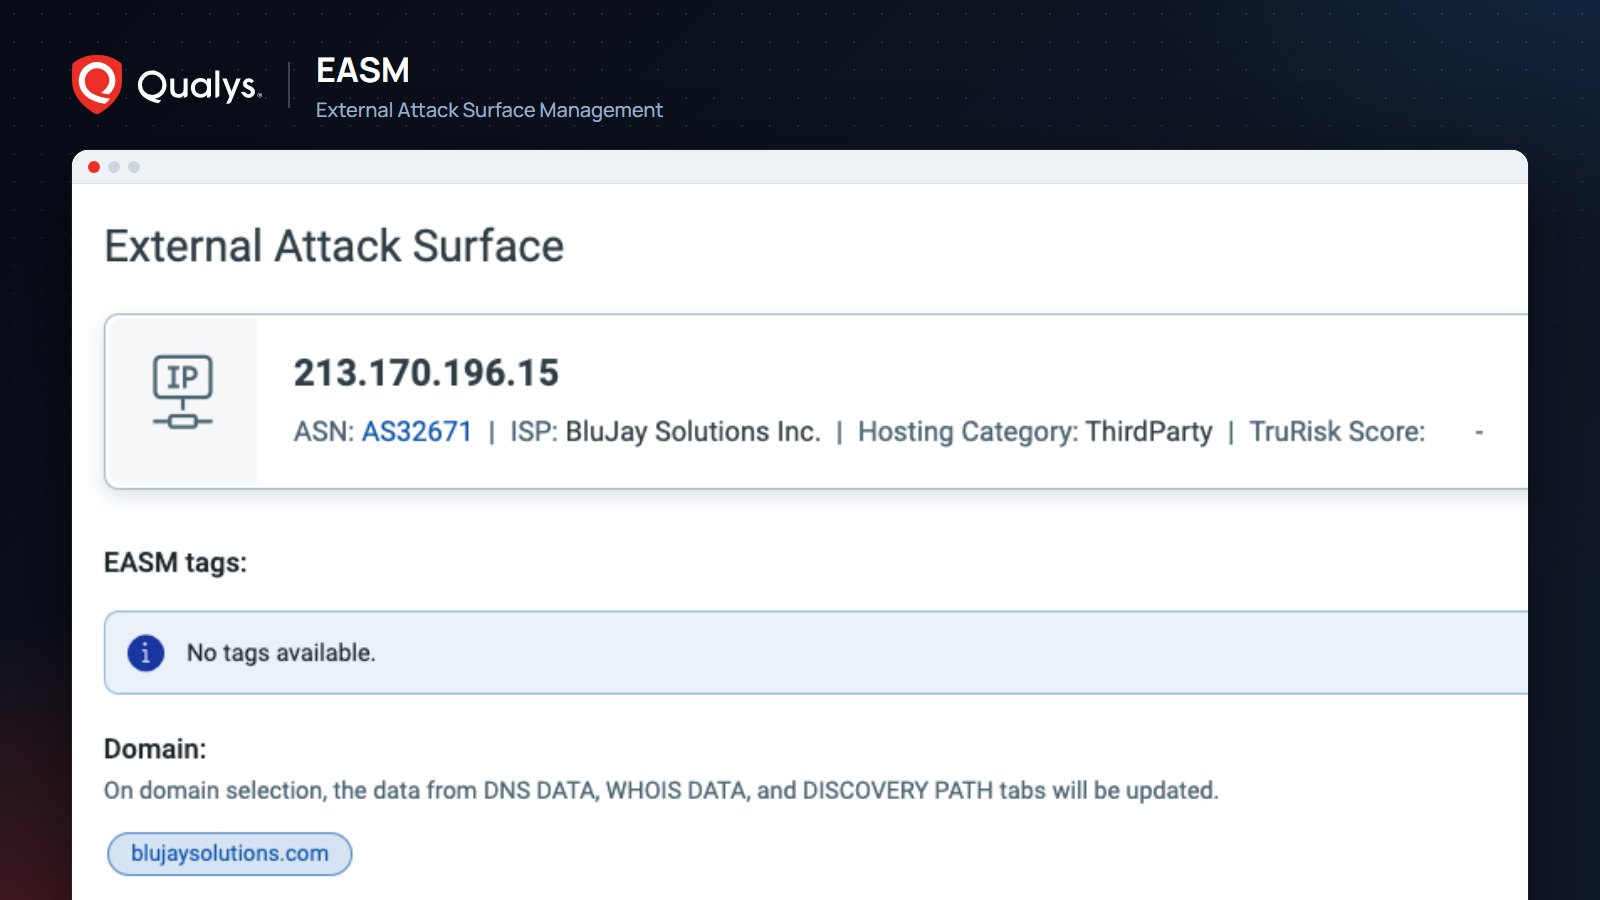
- Built-in EASM: External Attack Surface Management is natively integrated, so internet-facing assets live in the same view as your internal inventory.
- Measurable gains: Improve asset coverage by up to 30% by finding previously unknown assets, and stay audit-ready with an inventory that is always current.
“Where are our unsupported systems?”: An IT team runs the CSAM Tech Debt report to list end-of-support operating systems and unauthorized software with criticality and ownership attached. The records sync to the CMDB automatically, and the upgrade plan is built in order of risk.
How much do you really trust your asset inventory?
Komtera, Qualys's distributor in Turkey, brings a technical team that helps you position CSAM for your environment. Request a demo or a POC and see your unknown assets and tech debt in your own data.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.