
Qualys FIM (File Integrity Monitoring)
Real-time monitoring and alerting on file and directory changes, with detailed audit trails for compliance across on-premises, cloud and hybrid estates.
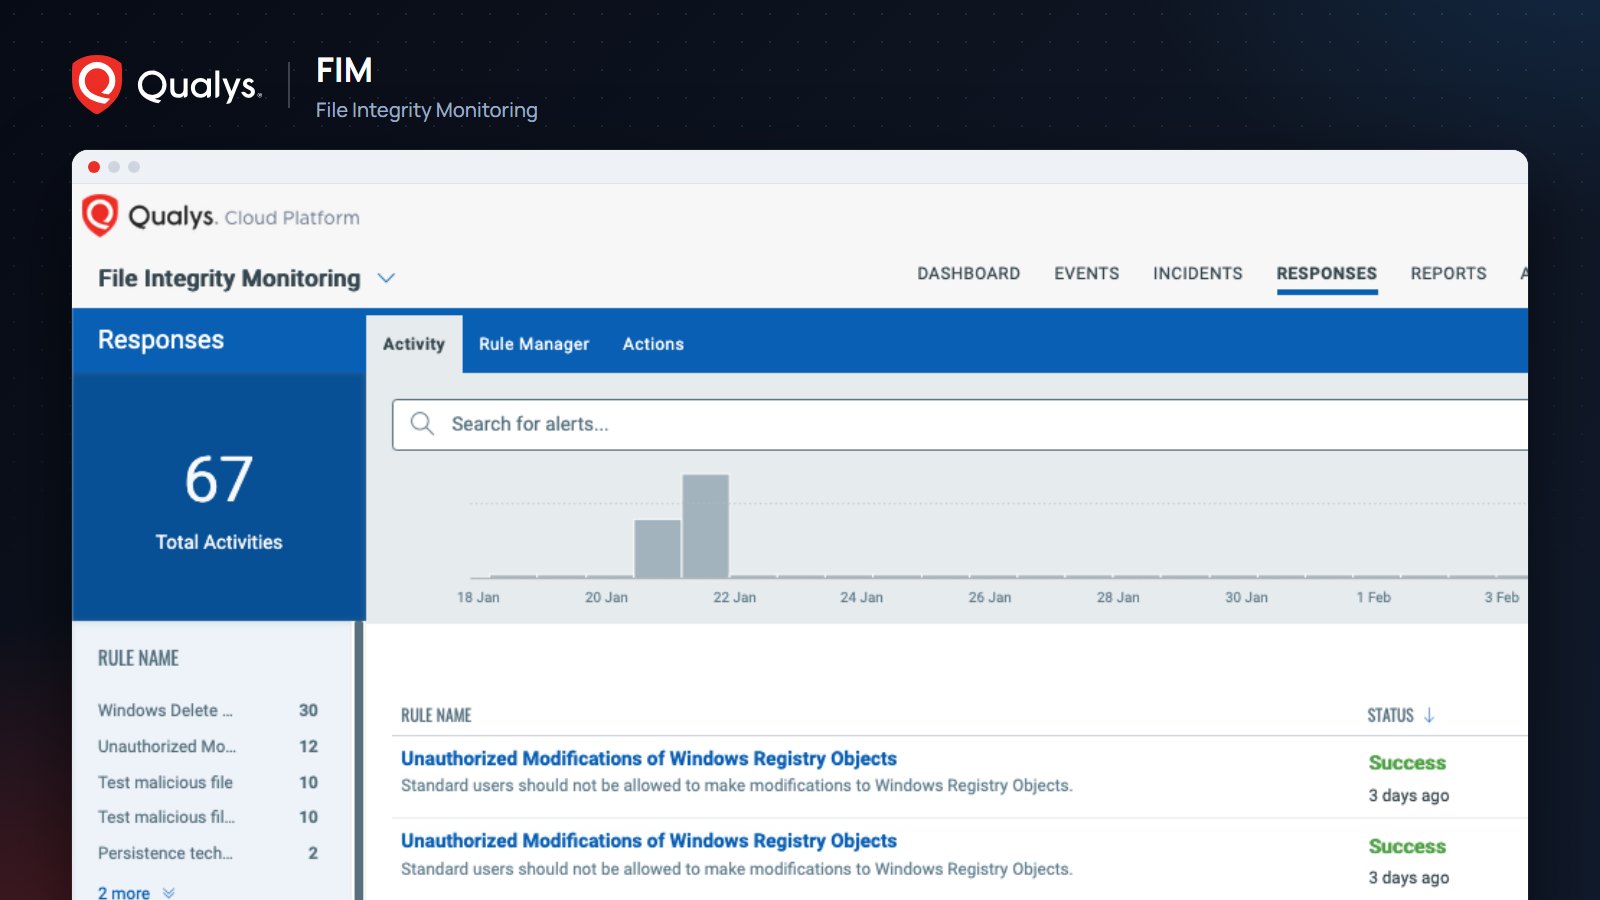
Qualys FIM (File Integrity Monitoring)
Know what changed in your critical files, and when, in real time.
An unnoticed change to critical system files or directories can be the first sign of unauthorized activity or a faulty change, and auditors expect proof of those changes. Qualys File Integrity Monitoring (FIM) monitors files and directories in real time, raises alerts on changes and keeps a detailed audit trail. It sits in the compliance layer of the Qualys Enterprise TruRisk Platform, alongside Policy Audit.
See every change that matters
FIM helps you meet the file-integrity requirements of government and industry standards while spotting unexpected or unauthorized changes quickly. There is no additional software to deploy: it runs on the Qualys Cloud Agent you already have.
- Real-time monitoring and alerts: Changes to files and directories are tracked as they happen and turned into alerts.
- Detailed audit trails: A detailed history of file changes simplifies compliance evidence.
- Rules and actions: Define what to watch with rules, and notify the right people through actions such as email alerts.
- Centralized dashboards and reporting: Monitor, analyze and report on events from one place.
- Broad coverage: Comprehensive monitoring for on-premises, cloud and hybrid environments.
How it works
- Agent: Qualys Cloud Agent; FIM is one of only two Cloud Agent components that touch kernel space (the other is EDR).
- Environments: On-premises, cloud and hybrid.
- Console: Dashboard, events, incidents, responses and reports in a single console.
- Compliance: Audit trails that support the file-integrity requirements of government and industry standards.
“Unexpected change on a production server”: Outside business hours, a critical configuration file on a production server is modified. FIM catches the change immediately, a predefined rule fires an email alert, and the team reviews the details in the audit trail before taking action.
Stronger together with Policy Audit
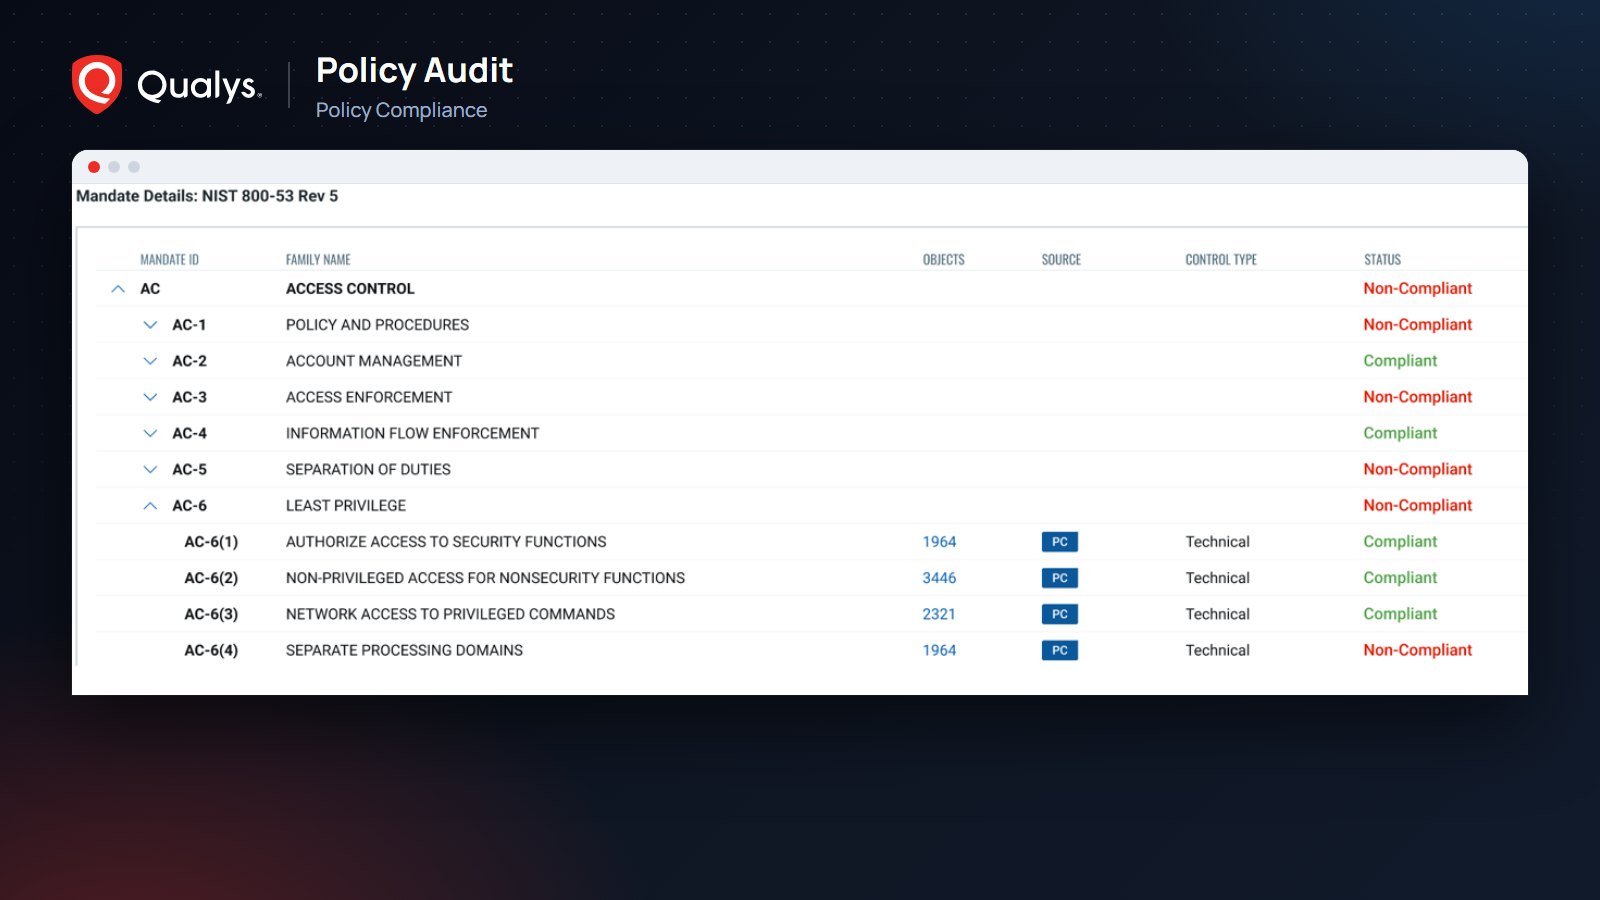
Policy Audit verifies that your systems are configured correctly against CIS, NIST and other standards; FIM watches what changes in those files and directories after hardening. Because both run on the same Qualys Cloud Agent and the same platform, compliance teams follow configuration posture and change history in one place and stay audit-ready.
Ready to make file integrity visible?
As Qualys’s distributor in Turkey, Komtera and its technical team help you design and deploy your FIM rules. Get in touch to request a demo or a POC.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.