
Qualys Policy Audit (Policy Compliance)
Automatically capture your hybrid environment's security and compliance posture against CIS, NIST, FedRAMP and other frameworks, and stay audit-ready.
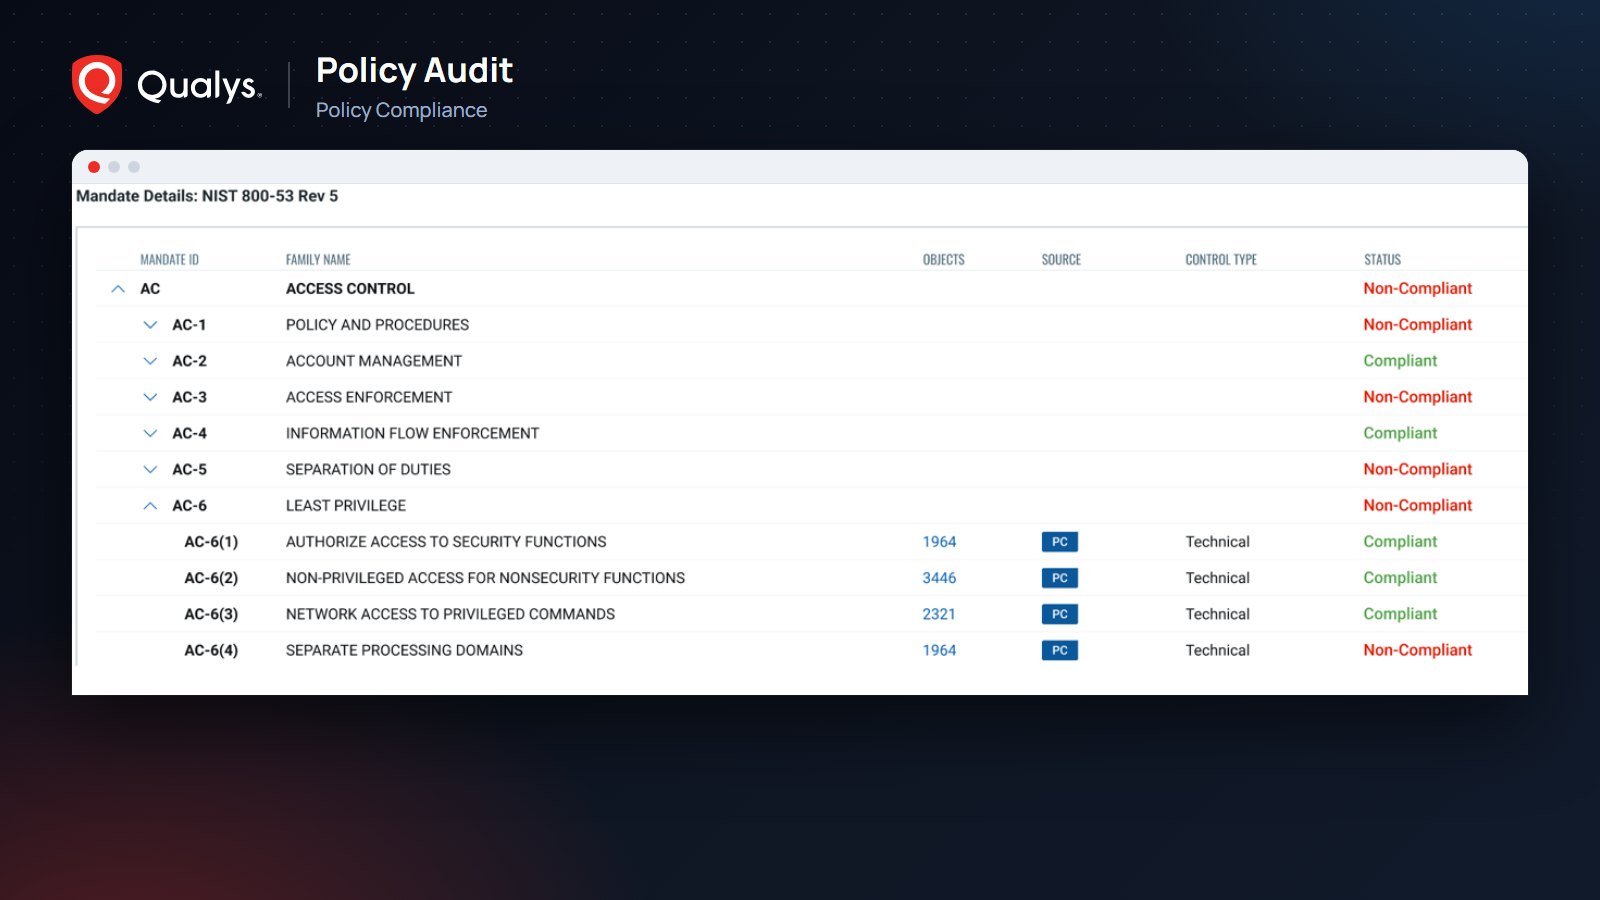
Qualys Policy Audit (Policy Compliance)
Move from configuration scanning to true configuration risk management, and stay audit-ready.
Misconfigurations in infrastructure, databases, web servers and middleware open doors for attackers just as surely as vulnerabilities do, while audit season eats weeks of team time. Qualys Policy Audit (Policy Compliance) automatically captures the security and compliance posture of your hybrid environment. It is the compliance pillar of the Qualys Enterprise TruRisk Platform, working from the same asset and vulnerability data.
From checklist scanning to configuration risk management
Policy Audit takes CIS scanning beyond a simple checklist and turns it into configuration risk management. An out-of-the-box assessment library and unified reporting cut the time, effort, cost and complexity of audits, and help organizations operationalize about 70% of the NIST Cybersecurity Framework.
- Out-of-the-box assessment library: Use industry best practices, frameworks and standards such as CIS, NIST and FedRAMP right away.
- Automated posture assessment: Configuration and compliance posture across your hybrid environment is measured continuously and automatically.
- Misconfiguration detection: Find misconfigurations across infrastructure, databases, web servers and middleware.
- CIS hardening: Harden systems according to CIS guidelines and verify policy enforcement.
- Regulatory dashboards: Unified dashboards for PCI DSS 4.0, SOX, HIPAA 2023, FINRA, GDPR, NYDFS, CCPA and others.
- Unified reporting: A single reporting dashboard makes assembling audit evidence far simpler.
Coverage and how it works
- Environments: Hybrid estates spanning on-premises and cloud.
- Data collection: The same Qualys sensors used across the platform; Cloud Agents, network scanners and scanner appliances gather compliance data alongside inventory and vulnerability data.
- Frameworks: CIS, NIST, FedRAMP and more.
- Reporting: Unified compliance reports for technical teams and auditors from one dashboard.
“Audit season without the scramble”: Ahead of a PCI DSS 4.0 audit, the team assesses the in-scope servers against ready-made CIS policies, routes deviations to system owners and pulls the evidence for the auditor from the unified dashboard in a single report.
Ready to make compliance a continuous process?
As Qualys’s distributor in Turkey, Komtera and its technical team help you design and roll out your Policy Audit policies. Get in touch to request a demo or a POC in your own environment.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.