
Qualys PCI Compliance (PCI DSS and Self-Assessment Questionnaire)
Automate PCI DSS scanning, vulnerability assessment and the Self-Assessment Questionnaire (SAQ), and stay compliant every day, not just at audit time.
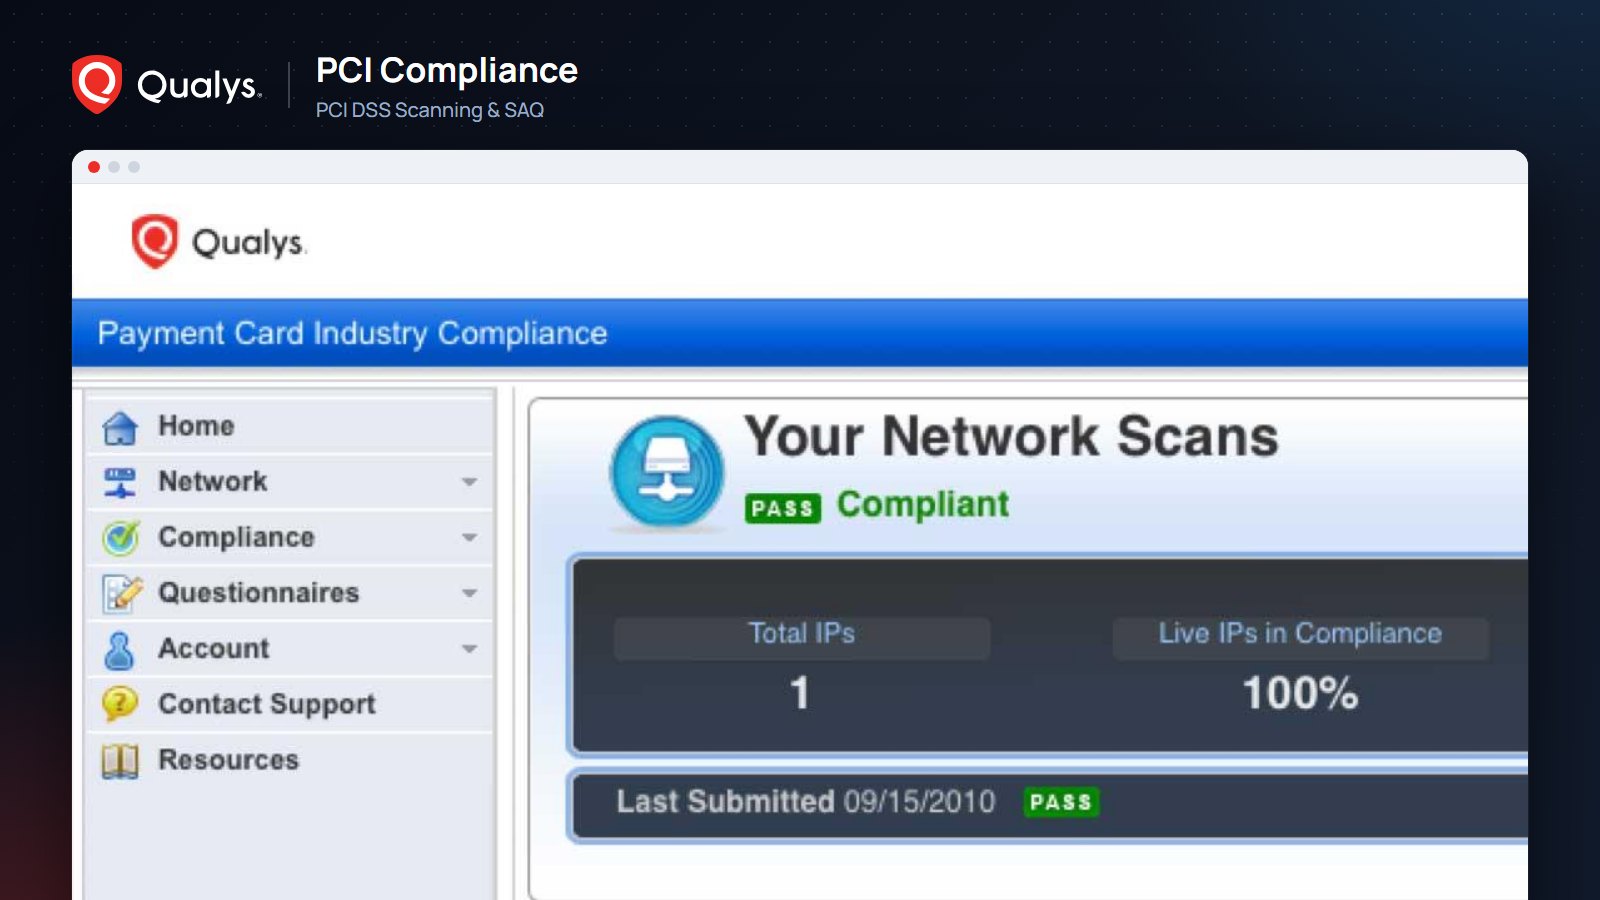
Qualys PCI Compliance (PCI DSS and Self-Assessment Questionnaire)
PCI DSS compliance isn’t an audit week. It’s an ongoing discipline, and Qualys PCI automates it.
Every organization that processes payment cards has to scan its systems regularly, fix vulnerabilities and document its compliance status for card networks and banks. Done by hand, that work is slow and leaves blind spots between audits. Qualys PCI Compliance brings PCI DSS scanning, vulnerability assessment and the Self-Assessment Questionnaire (SAQ) together in one workflow on the Qualys Enterprise TruRisk Platform.
Be audit-ready and stay compliant
Qualys PCI automatically scans the systems in your payment environment against PCI DSS requirements, reports the results and monitors compliance continuously, so your teams see and close risk without waiting for the next assessment.
- Automated PCI DSS scanning: Systems are scanned and assessed for vulnerabilities in the scope of PCI DSS automatically, removing the burden of planning scans by hand.
- Comprehensive reporting: Scan results and compliance status are presented in one reporting view, so technical teams and management share the same picture.
- Continuous monitoring: Compliance is not a point-in-time snapshot; your environment is monitored continuously so you remain compliant over time.
- Risk mitigation and vulnerability management: Detected vulnerabilities are prioritized and remediated, reducing the risk of a payment-data breach.
- Unified compliance view: Unified dashboards on the Qualys platform track PCI DSS 4.0 and other regulations from a single screen.
Self-Assessment Questionnaire (SAQ): self-assessment made simple
Qualys SAQ turns PCI DSS self-assessment into a guided process. Users step through the PCI DSS questions required to evaluate their security controls, with clear visibility into what has been answered and what is still open.
- The right SAQ type: Support for SAQ A, B, C and D ensures you use the version that matches your payment card processing method.
- Guided workflow: The required PCI DSS questions are presented in a streamlined flow that speeds up the assessment.
- Automated status reporting: Compliance status is reported automatically, progress is tracked and documentation is ready to submit to card networks and banks.
“Ahead of the annual assessment”: An e-commerce company’s security team scans its payment infrastructure with Qualys PCI on a regular schedule and closes the findings well before the assessment window. Meanwhile, the compliance lead completes the SAQ that fits the business’s payment method and shares the finished report with the acquiring bank, with no more weeks lost in spreadsheets.
Ready to simplify your PCI DSS program?
Komtera, Qualys’s distributor in Turkey, stands behind you with a dedicated technical team. Let’s plan together how Qualys PCI and SAQ fit your payment environment. Contact our team to request a demo or a proof of concept (POC).
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.