
Qualys EASM (External Attack Surface Management)
See your organization the way attackers do: discover unknown internet-facing assets and monitor risk across subsidiaries, vendors and M&A entities.
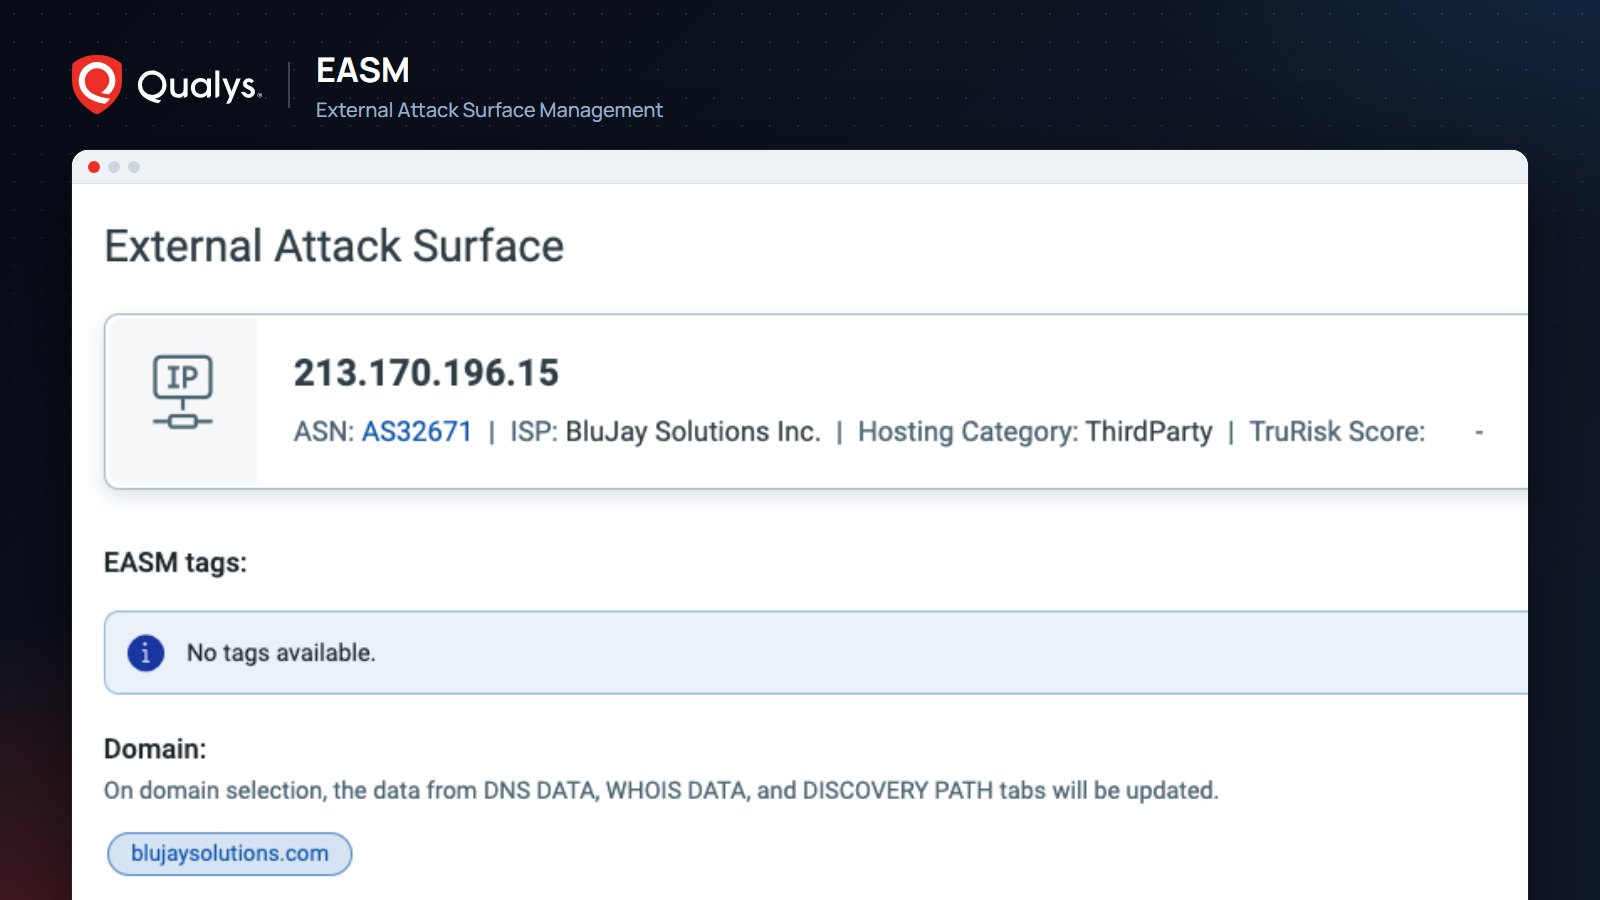
Qualys EASM (External Attack Surface Management)
Attackers see you from the internet. Qualys EASM lets you see every internet-facing asset before they do.
A forgotten campaign site, a test server nobody shut down, the domains of a newly acquired company: blind spots on the external attack surface rarely show up in the security team's inventory. Qualys External Attack Surface Management (EASM) discovers previously unknown internet-facing assets, domains and subdomains, and alerts you the moment new ones appear. It is natively integrated with CSAM on the Qualys Enterprise TruRisk Platform.
See beyond your own perimeter
EASM doesn't stop at your own network. It lets you monitor cyber risk across subsidiaries, third-party vendors and entities acquired through mergers and acquisitions, and it brings those findings into the same inventory and TruRisk prioritization as your internal assets.
- Unknown asset discovery: Surfaces internet-facing assets that are missing from your inventory.
- Continuous monitoring and alerts: Notifies you whenever a new unknown asset, domain or subdomain is found.
- Ephemeral asset visibility: Brings short-lived, internet-facing assets into view.
- Security gaps and misconfigurations: Identifies vulnerabilities and misconfiguration issues on exposed assets.
- TruRisk prioritization: Risk-based prioritization and remediation workflows keep the focus on the external exposures that matter most.
- One inventory with CSAM: Manages internal and external assets in a single, unified asset inventory.
How it works
Starting from a seed value such as your company name, EASM builds a discovery path that expands step by step through subsidiaries and related domains. For each asset you can review IP, ASN, hosting details and TruRisk score alongside external vulnerabilities, DNS and WHOIS data, SSL certificates and open ports on a single screen. Because the trail shows exactly how an asset was found, confirming ownership and routing it to the right team becomes straightforward. And because EASM is part of CSAM, a newly found asset can be classified, assigned an owner and queued for vulnerability scanning without ever leaving the platform.
“Due diligence before the deal”: A group of companies uses EASM to map the internet-facing assets of an acquisition target. Expired certificates and unnecessary open ports land on the remediation list before integration even begins.
Ready to see your external attack surface first?
Komtera, Qualys's distributor in Turkey, brings a technical team to help you deploy EASM and interpret the results. Request a demo or a POC and see your organization's external attack surface in your own data.
Talk to us about this solution
Reach out for licensing, architecture and technical requirements.